Find the AI risks no one’s checked yet.
Built for how AI actually fails, by industry
Lending, credit scoring, and fraud detection, audited for fair-lending exposure and model risk.
Trading, portfolio, and financial-reporting AI, reviewed for investment and reporting risk.
Clinical and patient-facing AI, reviewed for PHI handling and emerging state AI rules.
Underwriting and claims automation, tested for proxy discrimination and fairness.
Not sure where your AI stands?
Answer five quick questions and get a specific, real finding about your AI — free, in 60 seconds.
- No signup, no sales call, no pitch
- A straight read you can act on
- Across governance, data, bias, security & compliance
- Governance Medium
- Data provenance High
- Bias & fairness Low
- Security Medium
- Compliance High
Standards regulators actually recognize
Every audit is mapped to named, publicly recognized frameworks rather than an internal checklist of our own.
6 standards mapped
NIST AI RMF, ISO 42001, EU AI Act, HIPAA, SOC 2, India DPDP.
Independent auditors
Evidence-based findings, not self-graded checklists.
1–4 week reports
Clear findings with a prioritized fix list, not a data dump.
No payment upfront
Nothing is charged until you approve the audit scope.
AI audits, explained plainly
No jargon and no sales pitch. Just what an AI audit is, why it matters, who needs one, and how iDharma does it.
See how the audit works →An independent review of the AI systems you already use, checking how accurate, fair, secure, and compliant they really are rather than taking the vendor’s word for it.
Unaudited AI is unmeasured risk. Bias, security gaps, and compliance failures stay invisible until they cost you in fines, lost trust, or a regulator asking questions you can’t answer.
Any business running AI in a regulated or customer-facing process: lending, healthcare, hiring, or customer service, especially under EU AI Act, HIPAA, or SOC 2 obligations.
We independently test your AI against recognized standards like NIST AI RMF, ISO 42001, and the EU AI Act, then hand you a clear, prioritized report. Named auditor, cited methodology, no black box.
An independent read you can stand behind
Independent
A verified expert who didn’t build your AI reviews it. That independence is what makes the report defensible to a board or a regulator.
Standards-based
Measured against NIST AI RMF, ISO/IEC 42001, and the EU AI Act, so a finding traces to a named framework rather than a vendor’s say-so.
Actionable
A clear, prioritized report covering risks, compliance gaps, and a fix roadmap. It reads plainly instead of burying you in jargon.
Proof first
See the quality before you pay or talk to sales. The free 60-second Risk Snapshot hands you a real finding about your AI, no commitment required.
One quick check, a real finding
The free Risk Snapshot above is five plain-English questions — the same kind an auditor would ask first. Each answer maps straight to a real dimension of risk, not a generic score.
- Answer 5 plain-English questions
- See your governance, data, bias, security & compliance read
- Get one specific finding, not a vague grade
- Go deeper with a full audit if you want to
- Governance Medium
- Data provenance High
- Bias & fairness Low
- Security Medium
- Compliance High
Data provenance: High. Document where your AI’s training & input data comes from before any regulated decision.
A report a board can act on
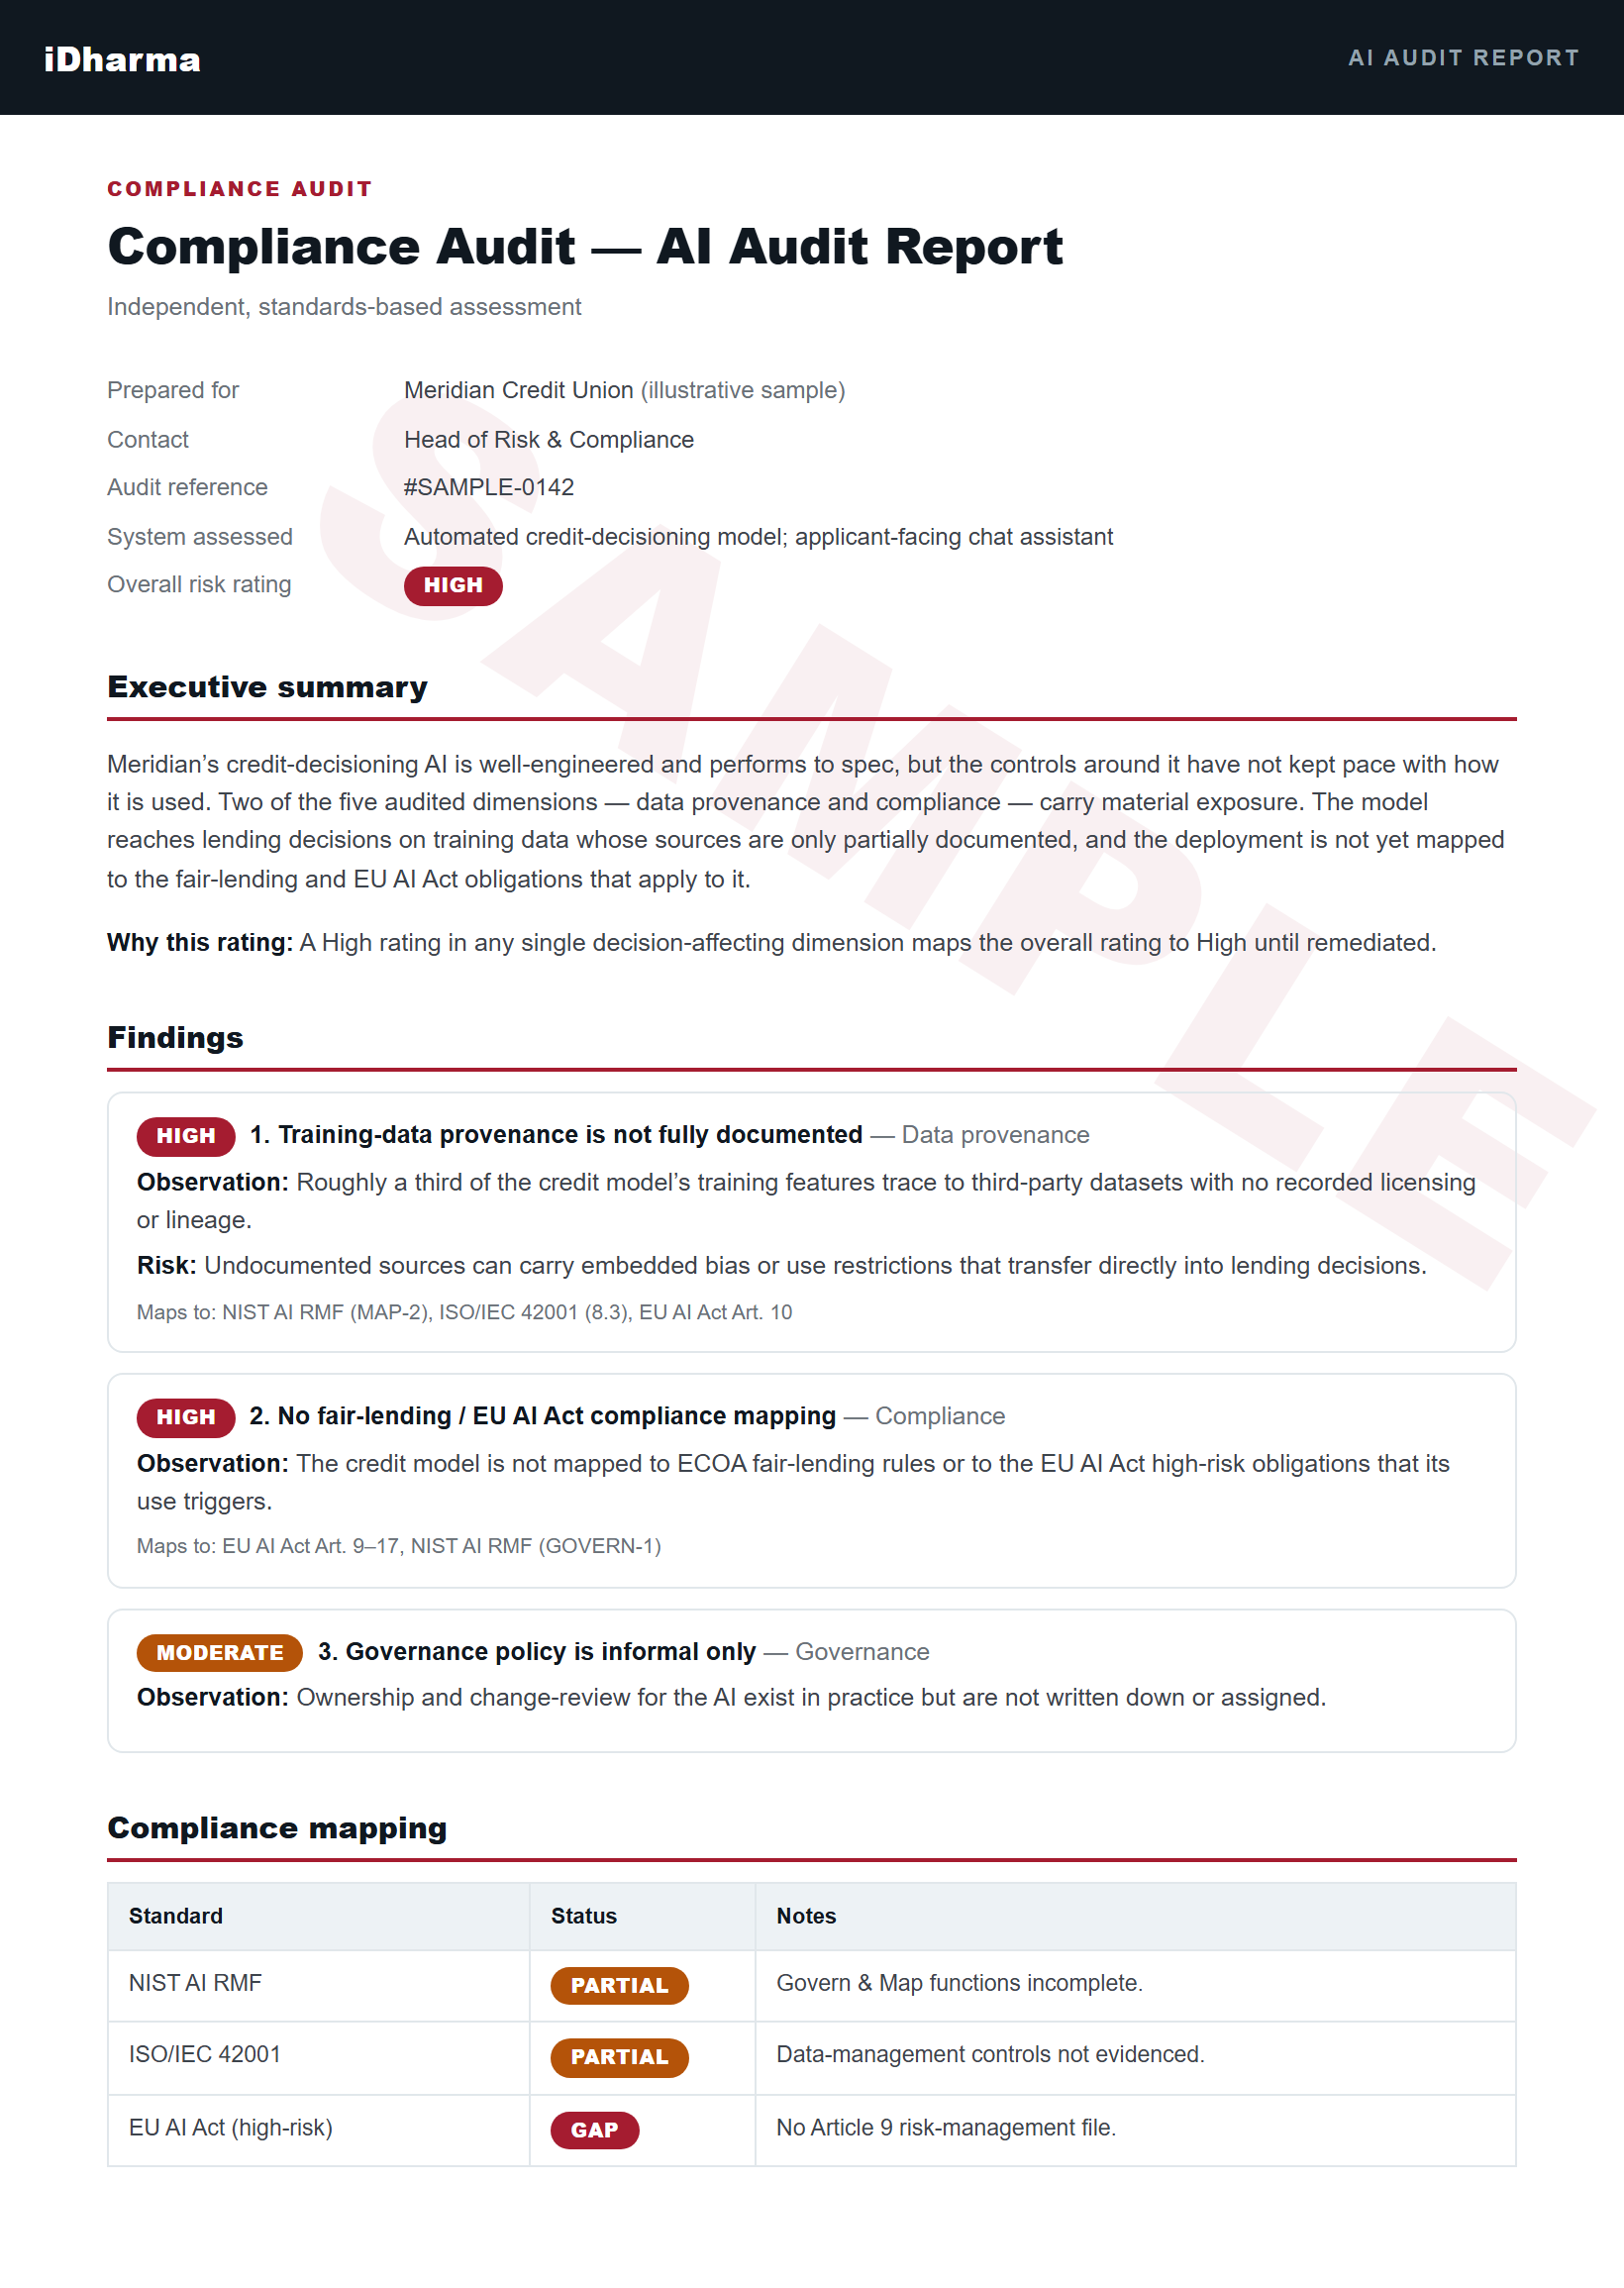
This is the actual output of an iDharma audit: a clear read your board, a partner bank, or a regulator can rely on.
- Findings ranked by severity
- Each one mapped to the standards that apply to you
- A plain-English executive summary
- A prioritized fix roadmap, signed by a named auditor
Choose the depth your AI needs
Transparent, fixed-scope pricing — scoped with you before anything is charged. No payment until you approve the scope.
A fast, focused review of your core AI system, with the top risks surfaced.
A deeper audit mapped to the standards and regulations you answer to.
Our most thorough review, including threat scenarios and a full roadmap.
We’d rather prove competence than claim it
We publish public teardowns of real AI enforcement cases — what went wrong, and what an audit should have caught. Our methodology is published and openly dated, so you can see it stays current.
iDharma’s Mission
Businesses are adopting AI faster than anyone can verify it. Most teams cannot say, with evidence, whether the AI they rely on is accurate, fair, secure, or compliant.
iDharma closes that gap. We independently audit the AI you already run against recognized standards like NIST AI RMF, ISO/IEC 42001, and the EU AI Act, then deliver a clear, prioritized report.
No black box and no vendor spin: a named auditor, a cited methodology, and a straight answer on where your AI stands and what to fix first.
Every iDharma audit is led and signed by a named reviewer — you’ll always know exactly who examined your AI and why we reached the conclusions we did. No black box, no anonymous “team.”
Know your AI is trustworthy
An independent iDharma audit shows you where your AI holds up on accuracy, fairness, security, and compliance, then tells you what to fix first.